
Network security for businesses
We protect the infrastructure, not just the perimeter: next-generation firewalls, segmentation, access control, secure remote access and monitoring from our NOC.
Layered security
- Internet
- NGFW
- Core
- Segments
- Access control
- NOC
- NGFW
- IPS/IDS
- 802.1X
- RADIUS
- WPA3 Enterprise
- IPSec
- MFA
- ACL
- SD-WAN
- HA
- SNMP
- Syslog
Diagnosis
What we find, and what we do
Most networks we audit work. The problem is everything they can see and let through without anyone knowing.
What we find
What we do
Every device can see every other
We segment by VLAN: users, servers, infrastructure, IoT and guests, and the firewall decides what passes between them.
A firewall with rules nobody remembers
We audit the policies, strip out what isn’t needed and leave only what is, documented.
Guests browse on the company network
An isolated guest network, with client isolation and no access to anything internal.
Remote working with access open to the internet
VPN for every user and permissions based on what each person needs.
Cameras and IoT on the corporate network
Each type of device on its own segment and never exposed to the internet.
If the carrier goes down, the office stops
Multi-WAN with 5G or Starlink backup and automatic failover.
What we do
Security at every layer of the network
On the network you already have or on a new one. Always with a written plan before we touch anything.
Network audit
Topology, firewall rules, remote access, Wi-Fi and equipment: the real state, the risks and what to fix first.
Firewall and policies
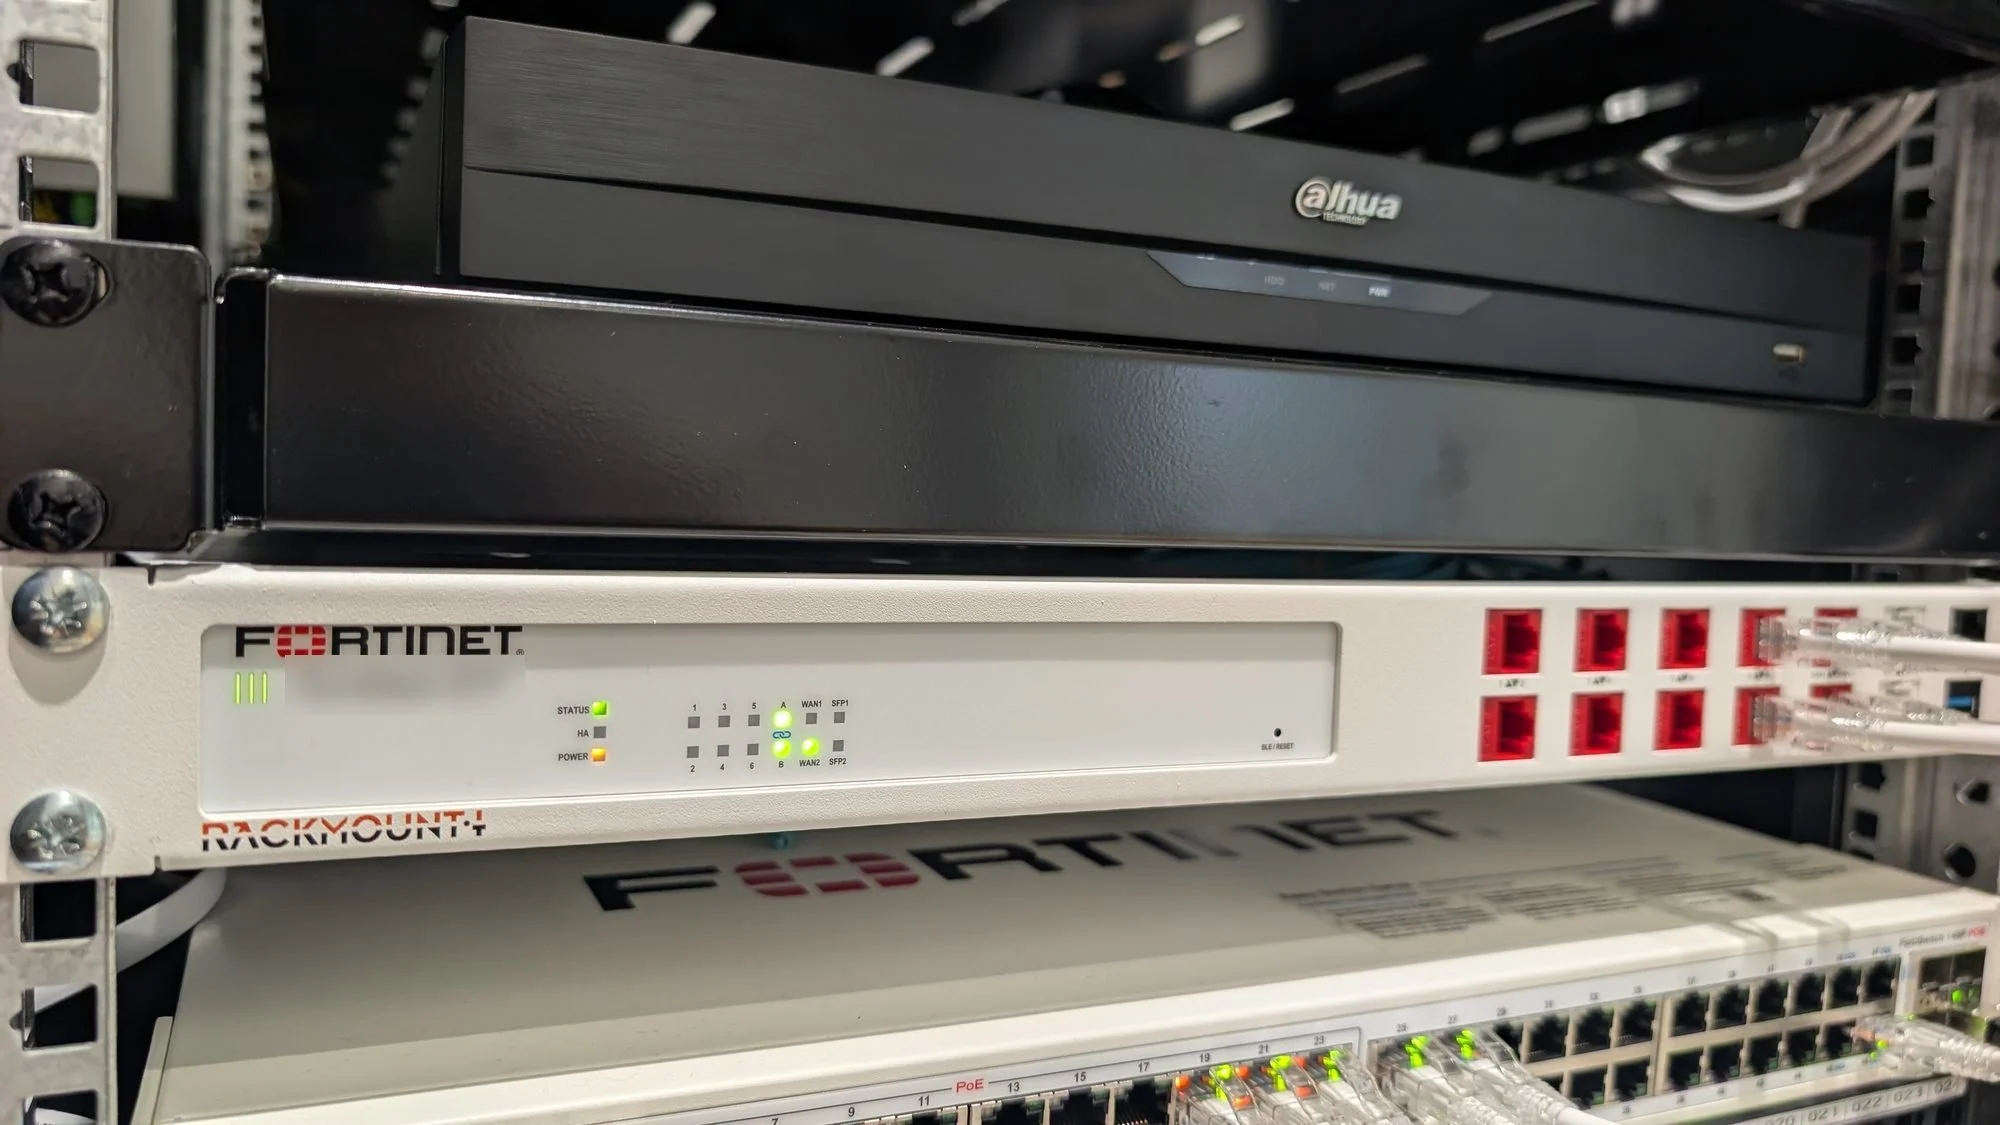
Fortinet and Palo Alto Networks next-generation firewalls: IPS/IDS, application control, web filtering, DNS security, SSL inspection, Geo-IP and granular rules. A minimal, understandable, auditable and documented policy.
Segmentation
Networks separated by VLAN, inter-VLAN routing and ACLs: each environment sees only what it should.
Site-to-site VPN
Encrypted IPSec tunnels and SD-WAN to join offices as if they were a single network.
Secure remote working
Per-user VPN remote access, without opening internal services to the internet.
Monitoring and alerts
Watching the firewall, links and devices, with alerts when something changes.
Network access control
Who and what connects to the internal network: 802.1X, RADIUS, per-user or per-device authentication and dynamic VLAN assignment.
Wi-Fi security
WPA2/WPA3 Enterprise with 802.1X, separate networks for staff, IoT and guests, and guests isolated from the corporate network.
Logging and traceability
Centralised firewall and network device logs when the project calls for it: which device, which communication, which policy and when.
In detail
How we solve it
Next-generation firewall
More than opening and closing ports
We configure firewalls that inspect traffic: they stop known attacks, control which applications are used and filter browsing, with rules designed for each network segment.
- IPS and application control
- Web filtering
- NAT, DHCP and VPN
- Minimal, documented rules
Segmentation
Every environment on its own network
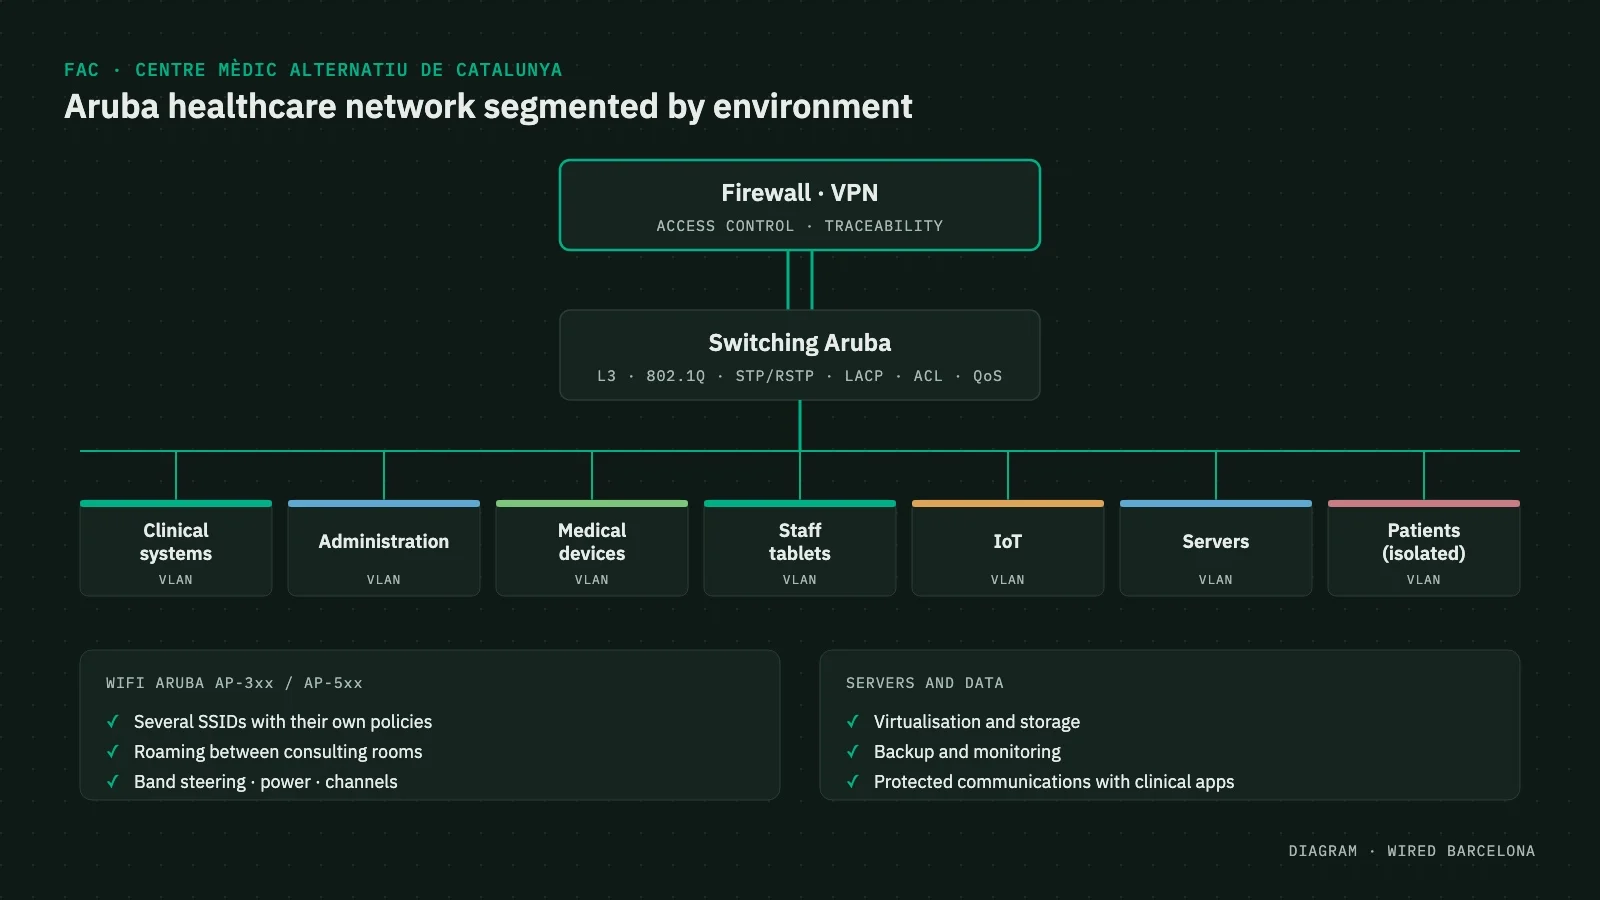
In a healthcare centre like FAC we separate clinical systems, administration, medical devices, tablets, IoT, servers and patients. One compromised device doesn’t drag the rest down with it.
- 802.1Q VLANs and inter-VLAN routing
- ACLs between segments
- Guests and patients isolated
- IoT and cameras on their own segment
Continuity
If the carrier goes down, the network keeps going
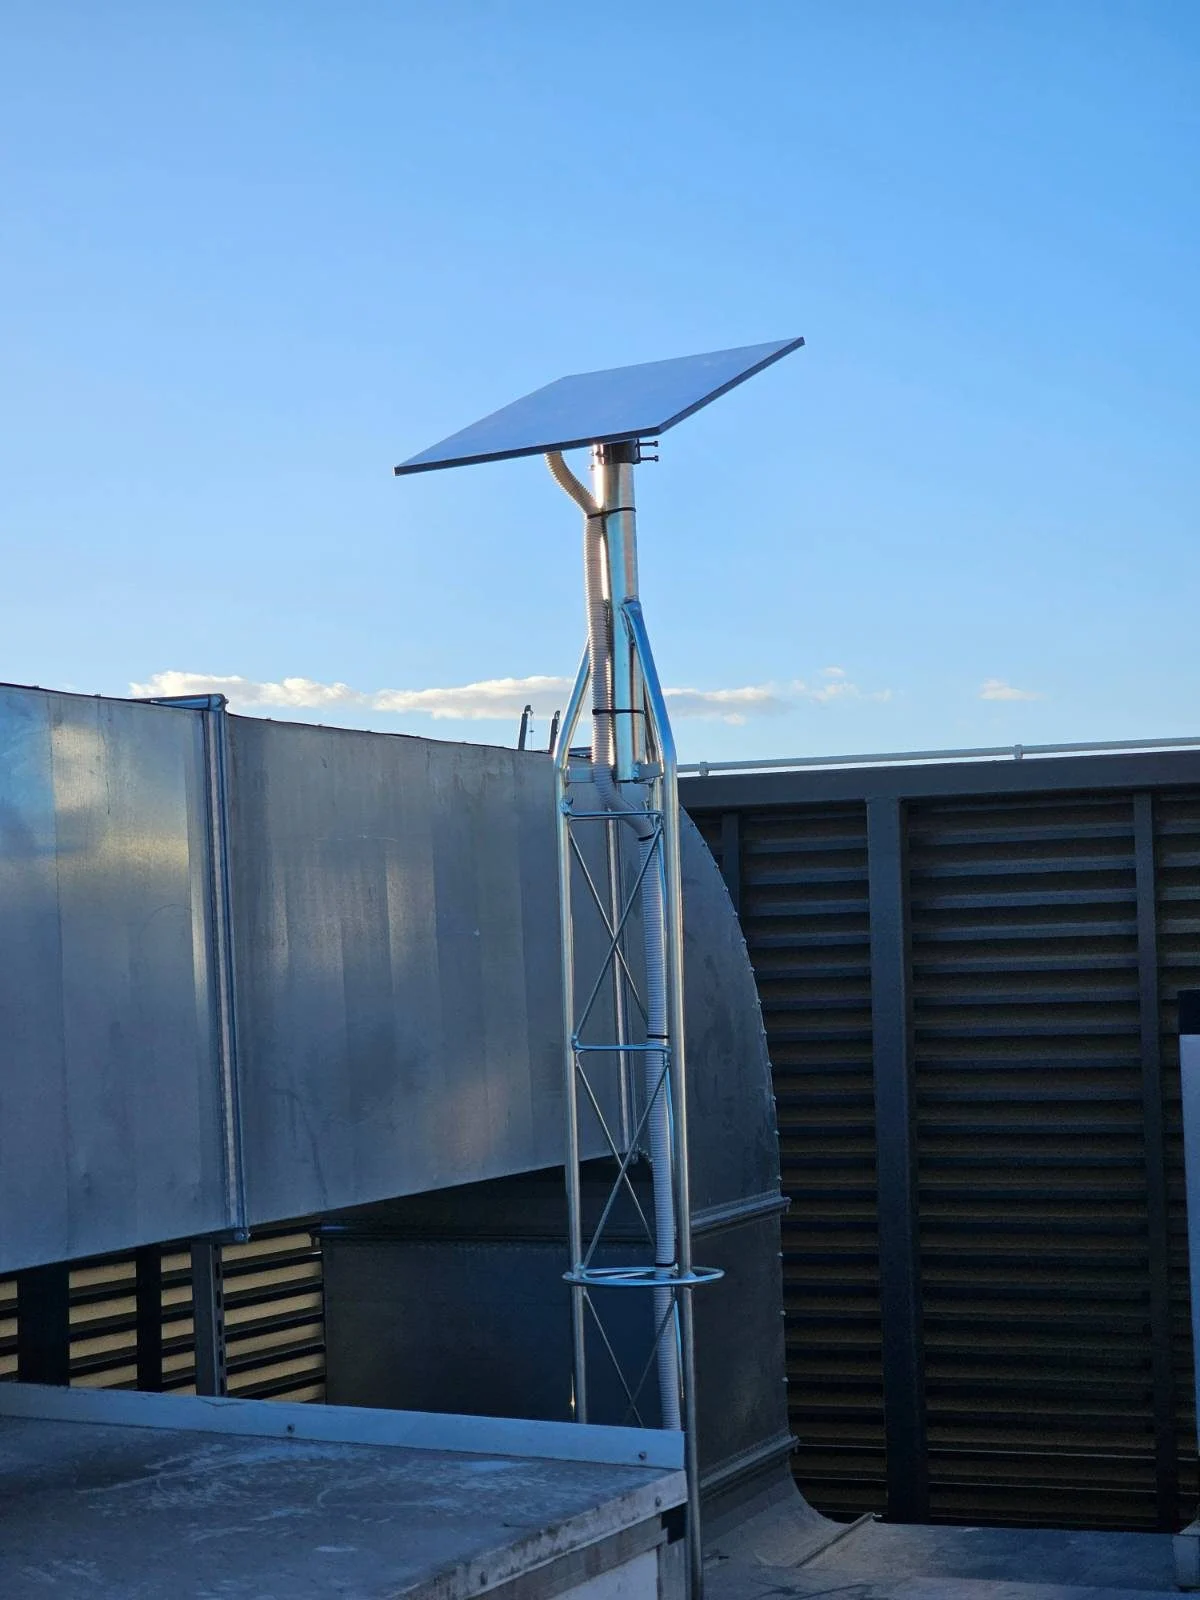
Security is also availability. We design redundant internet with 5G or Starlink backup and automatic failover when the main link fails.
- Multi-WAN with fibre, 5G and Starlink
- Link monitoring
- Tested failover and failback
Also with high-availability firewalls and dual carriers. We test the failure scenarios before signing off the redundancy.
Example
A typical office, segmented
Every segment goes through the firewall and only talks to what its policy allows.
Firewall
Workstations
Internet, servers and company applications.
Servers
Only the services they publish, only to those who use them.
Guests
Internet only, isolated from everything else.
Cameras and devices
Only to their recorder, no internet access.
Management
Network equipment administration, only from authorised workstations.
Network security audit
A technical snapshot before we touch anything
Before changing an infrastructure, we analyse its real state. The outcome: the risks found and the recommended actions, in order of priority.
- Topology and segmentation
- Firewall rules and objects
- Services published to the internet, NAT and port forwarding
- VPN and remote access
- Users and authentication methods
- Wi-Fi networks
- IoT and CCTV
- Firmware on infrastructure equipment
- WAN redundancy and connectivity
Case study
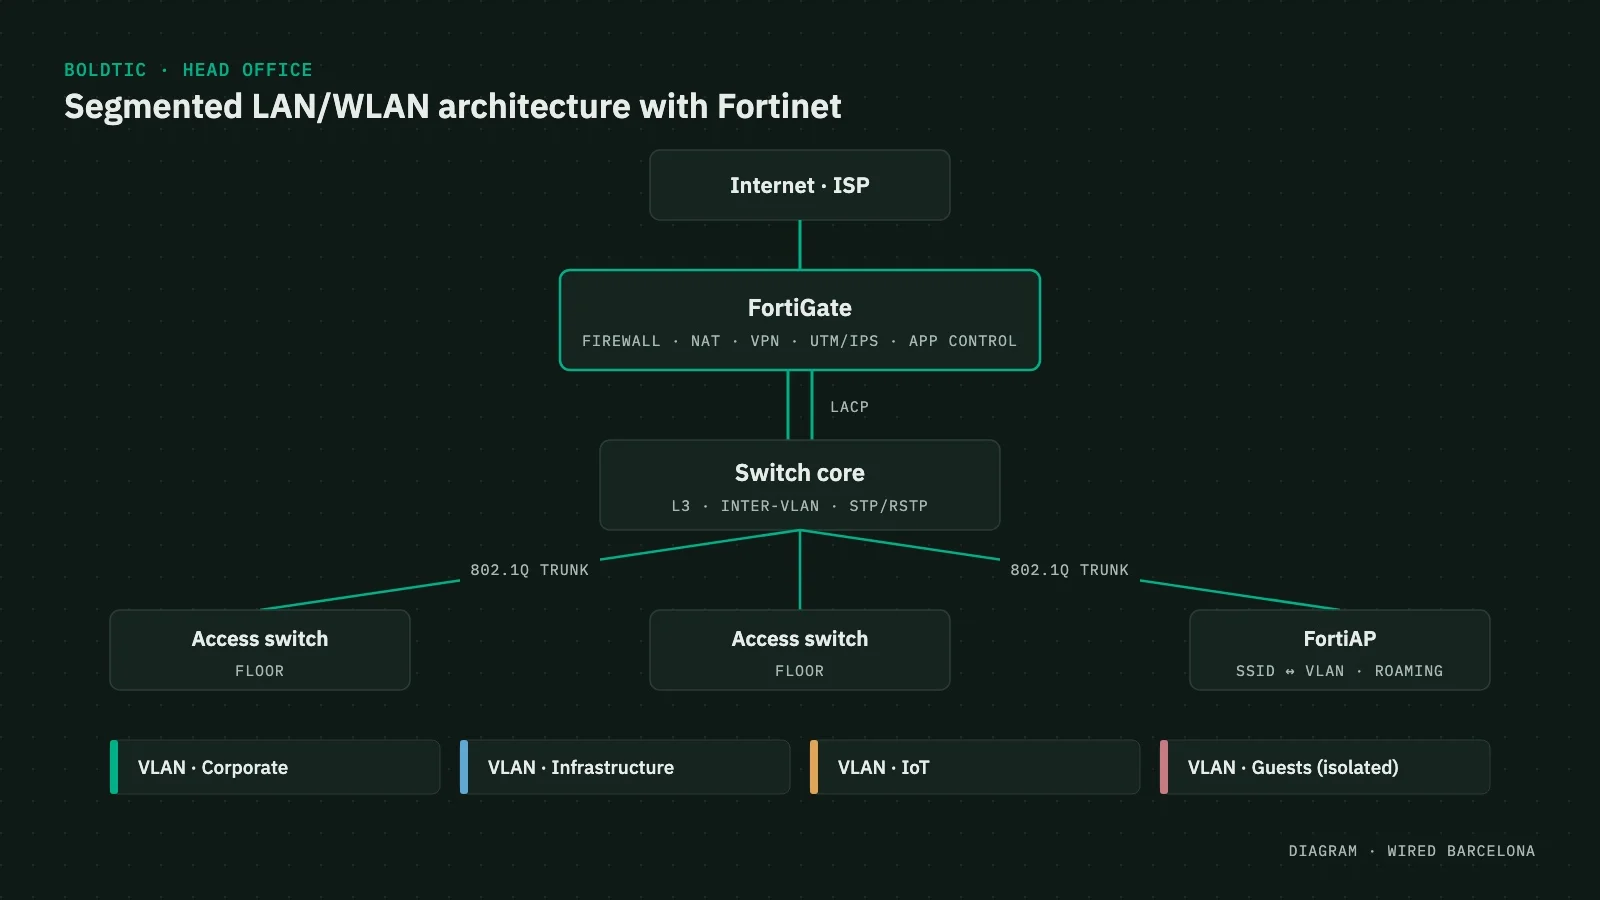
Boldtic: the whole network rebuilt, without stopping the office
We redesigned their head office network with Fortinet: four separate networks, a firewall with UTM/IPS and application control, and a controlled migration on the live network.
Platform
Fortinet
Separate networks
4
Security
UTM / IPS
Migration
In production
What you get
When we finish, the security is in writing
- Audit report with prioritised risks
- Segment and firewall policy design
- Documented firewall and VPN configuration
- Network and addressing diagram
- Migration plan with its tests
How we work
From audit to operations
We audit
The existing infrastructure, configurations, access and communications.
We design
Segmentation, policies, authentication, remote access and redundancy.
We implement
Firewall, switching, VLANs, VPN, Wi-Fi and security mechanisms.
We validate
Allowed and blocked traffic, remote access, redundancy and failure scenarios.
We document
Diagrams, addressing, segments, policies, VPN and relevant configurations.
We monitor
The infrastructure can be brought into our NOC for continuous monitoring.
Visibility
We don’t wait for a user to tell us something’s wrong
From our NOC we monitor firewalls, switches, routers, access points, WAN links, VPNs and site-to-site connectivity: availability, errors, latency, packet loss, CPU and memory, with alerts on outages and degradation.
Projects
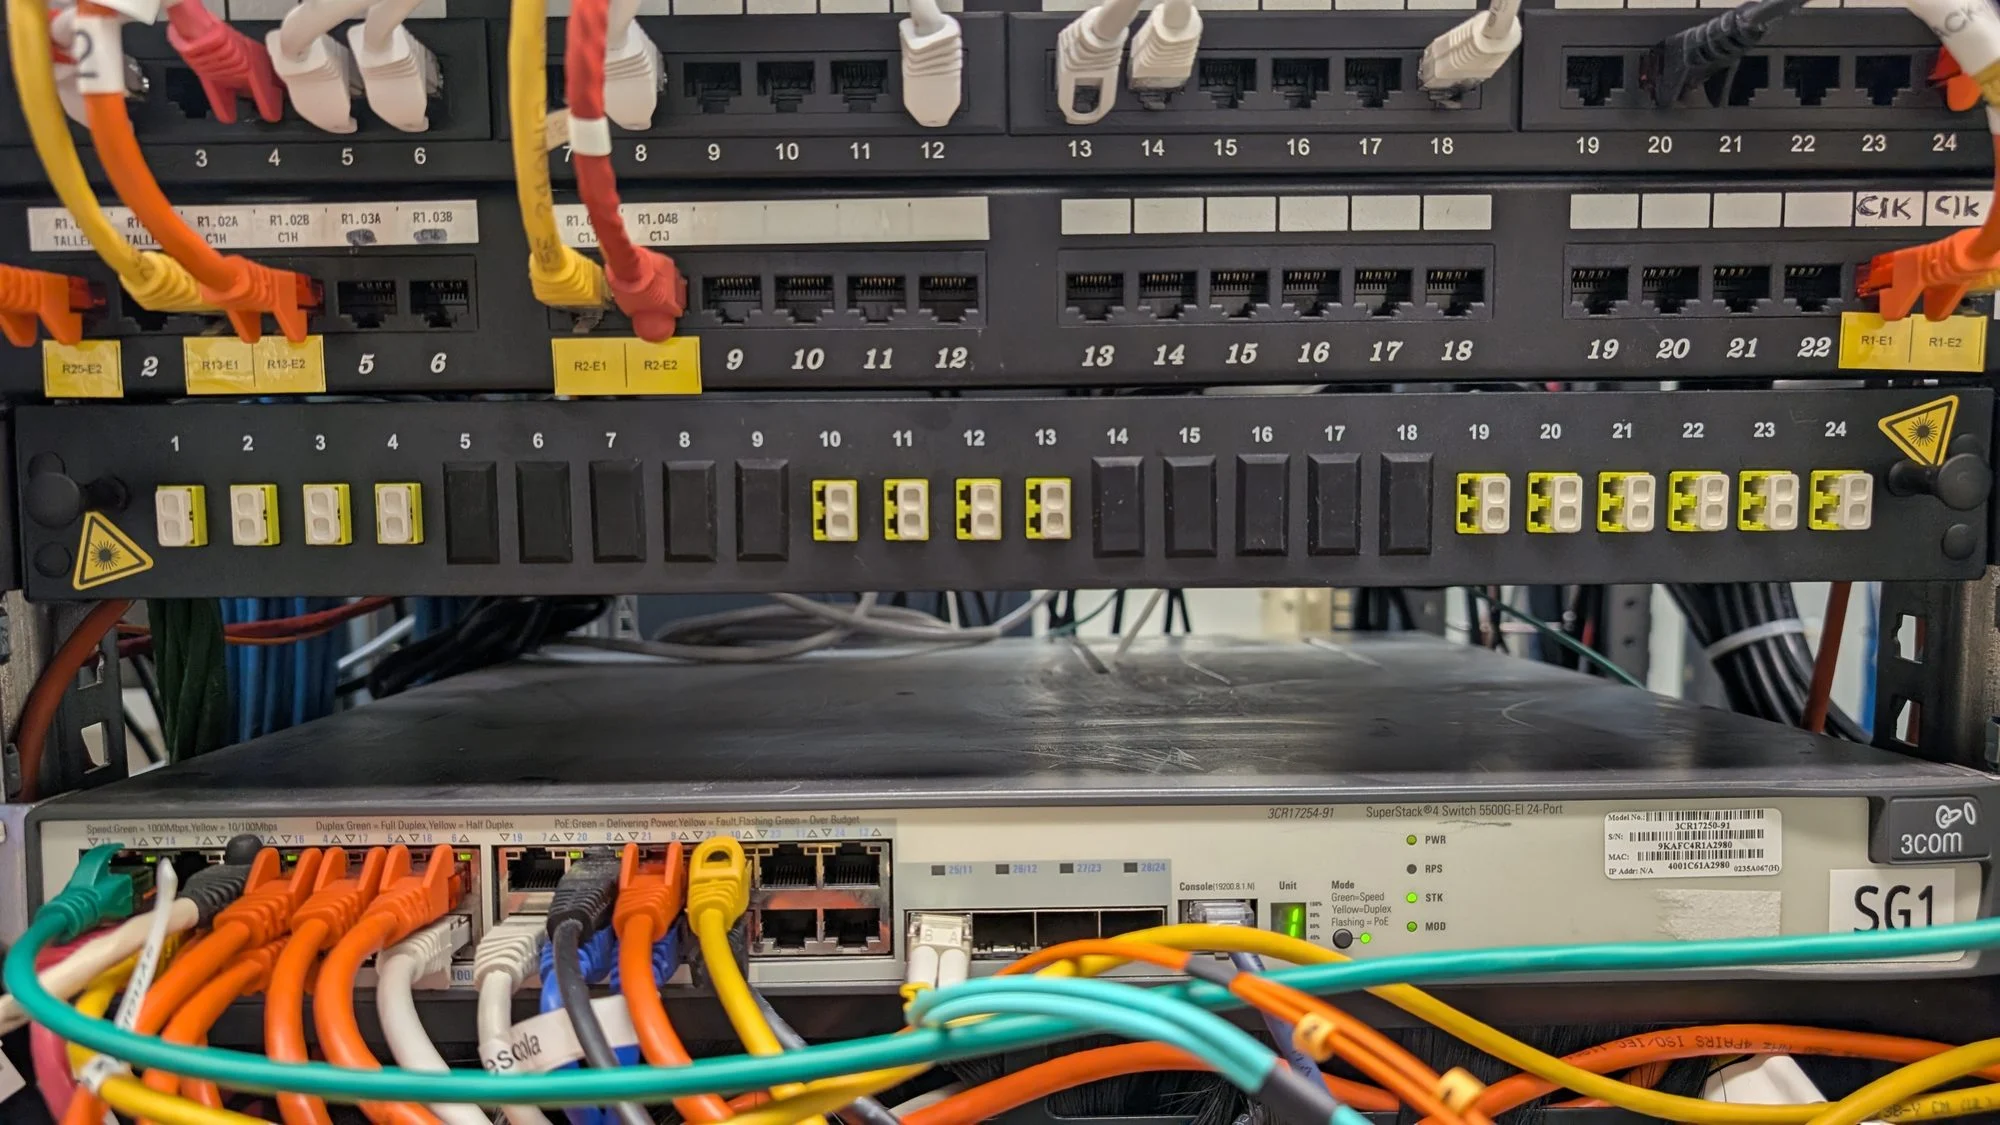
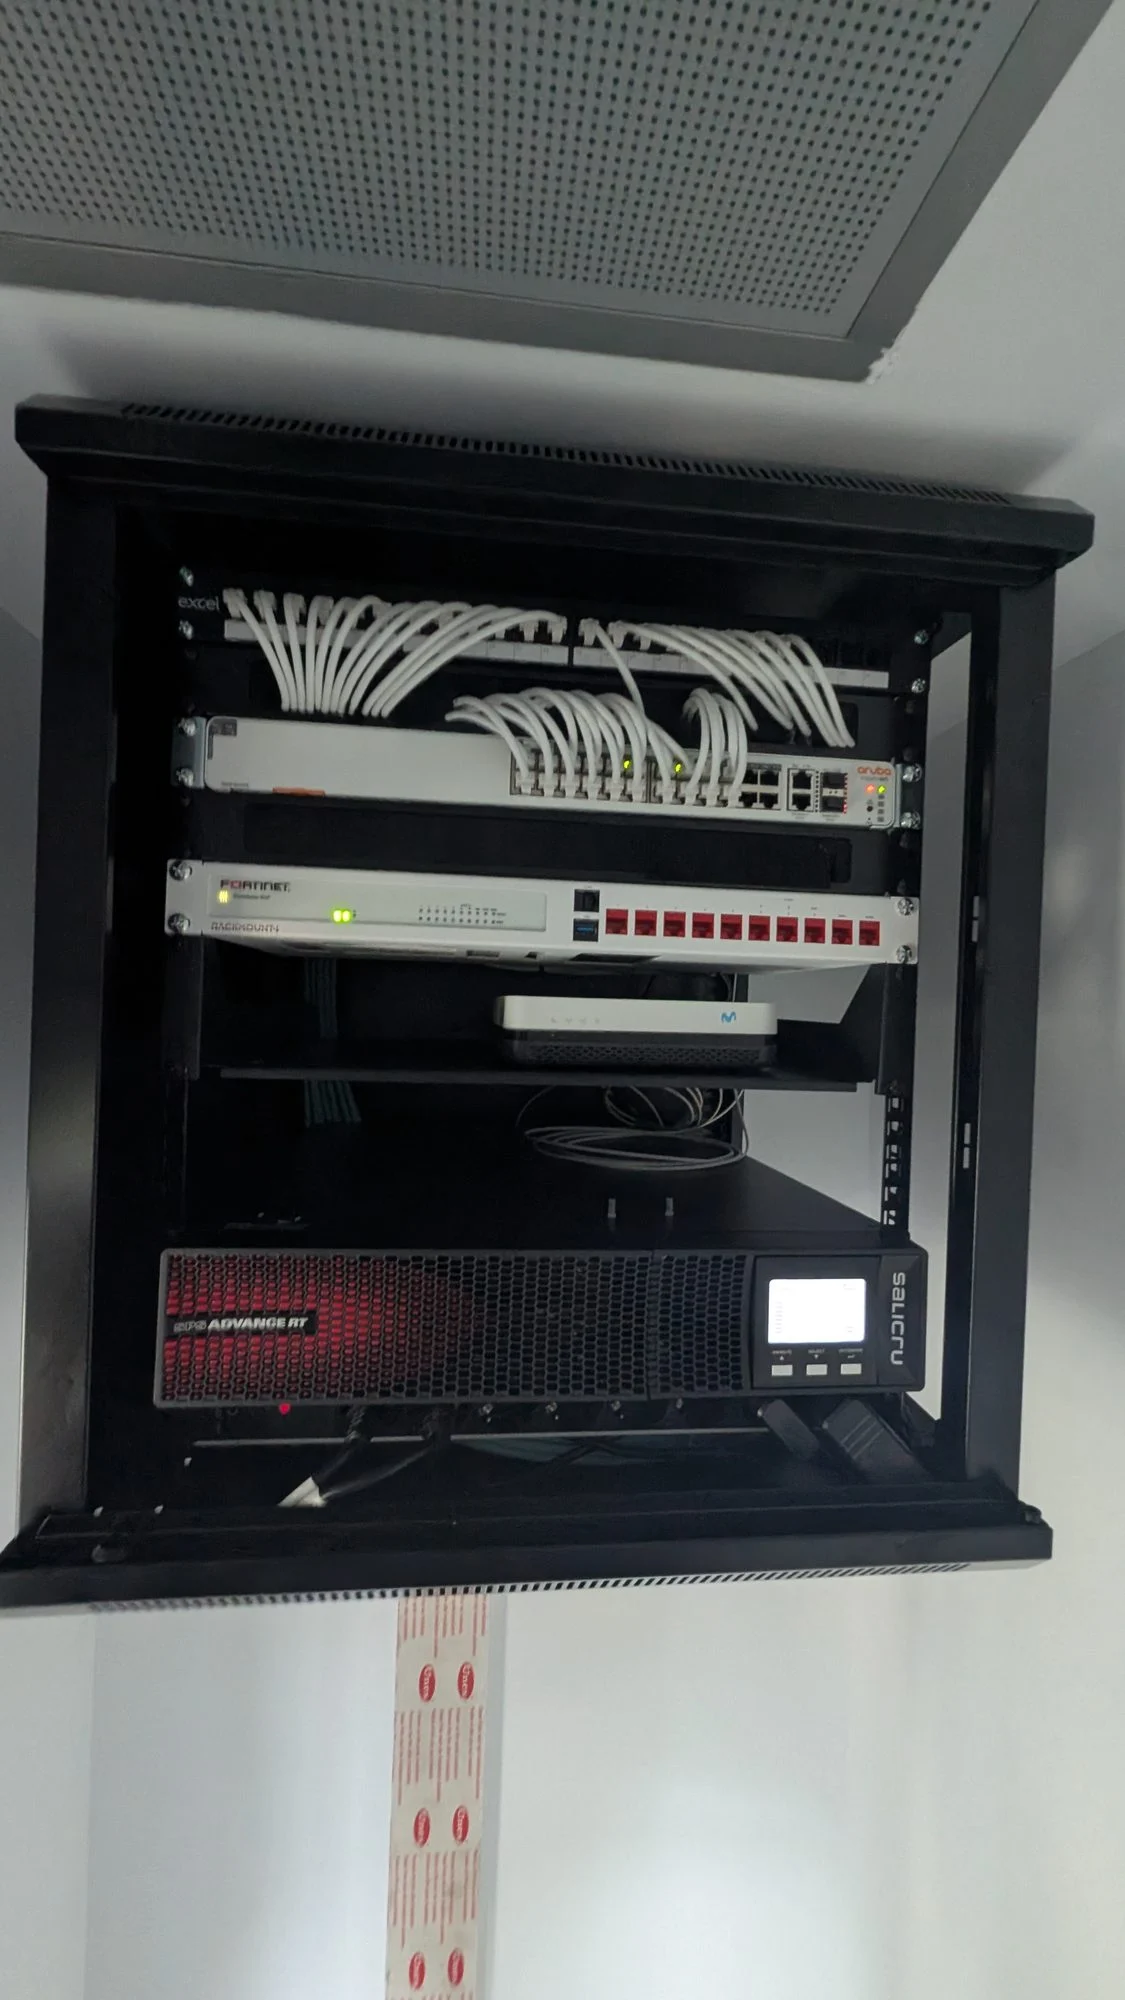
Security and network projects
FAQ
Can you review a firewall we already have?
Yes. We audit Fortinet, Palo Alto Networks and other vendors’ firewalls: rules, NAT, VPN, remote access and segmentation. You get the real state, the risks and what to fix first.
Do the changes take the network down?
We plan changes in phases and in windows agreed with you, testing before signing off each step. At Boldtic we migrated the entire network with the offices fully operational.
Which vendors do you work with?
Mainly Fortinet and Palo Alto Networks for firewalls, alongside Cisco, HPE Aruba Networking and RUCKUS for switching and Wi-Fi. We choose the technology to fit the project’s architecture and requirements: we don’t design the project around a brand.
What documentation do we get?
The network documentation: diagram, addressing, VLANs, firewall rules and remote access.
What happens if the internet goes down?
We design redundant internet: the main link with 5G or Starlink backup and automatic failover. At one corporate office we manage, for example, there are three backups.
Tools
Which attacks would your defences stop?
Switch on the defences you have today, launch four attacks that come in through different paths and see which are stopped. Or check your network and your email protection in minutes. And if you want to understand why segmentation is key to stopping an attacker inside the network, read our network segmentation guide.
Related services